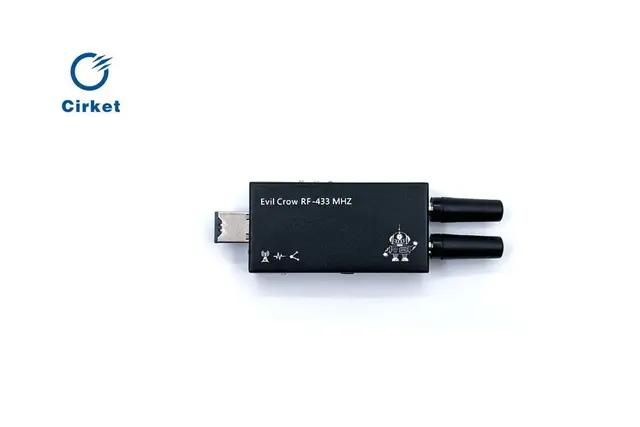
EvilCrowRF V2 RF Brute-Force Firmware for Fixed-Code Systems
Dedicated brute-force firmware for Evil Crow RF V2 targeting 34+ fixed-code RF protocols including CAME, Nice FLO, Princeton, and Chamberlain across 300-928 MHz with precise OOK timing.
Overview
A specialized brute-force firmware for the Evil Crow RF V2 by realdaveblanch that systematically transmits every possible code combination against fixed-code wireless systems. It targets garage doors, gates, and alarm systems that use legacy fixed-code RF protocols without rolling code protection.
Supported Protocols
The firmware targets 34+ protocols across multiple frequency bands:
433.92 MHz (Europe)
- CAME — 12-bit and 24-bit Manchester encoding
- Nice FLO — fixed code with PWM modulation
- Clemsa Mastercode — PWM-based encoding
Tristate Systems
- Princeton PT2262 — ternary logic (0, 1, Float)
- SMC5326 — 25-bit tristate
315/300 MHz (Legacy USA)
- Chamberlain Security+ 1.0
- Linear MegaCode
- Firefly — DIP switch systems
868.35 MHz (High Security)
- Hörmann HSM4
- Marantec Digital
How It Works
The firmware uses On-Off Keying (OOK) modulation to transmit raw RF bursts representing binary or ternary data. Each protocol's timing requirements (typically 300-700 microseconds per bit) are precisely encoded, and the firmware iterates through the complete keyspace.
Attack time formula: Total Time = Number of Codes x Frame Duration x Repetitions
For example, a 10-bit binary system takes approximately 1,024 iterations x 20ms x 3 repeats = ~61 seconds to exhaust.
The ESP32's dual-core processor and the CC1101 transceiver's precision timing enable microsecond-accurate signal synthesis.