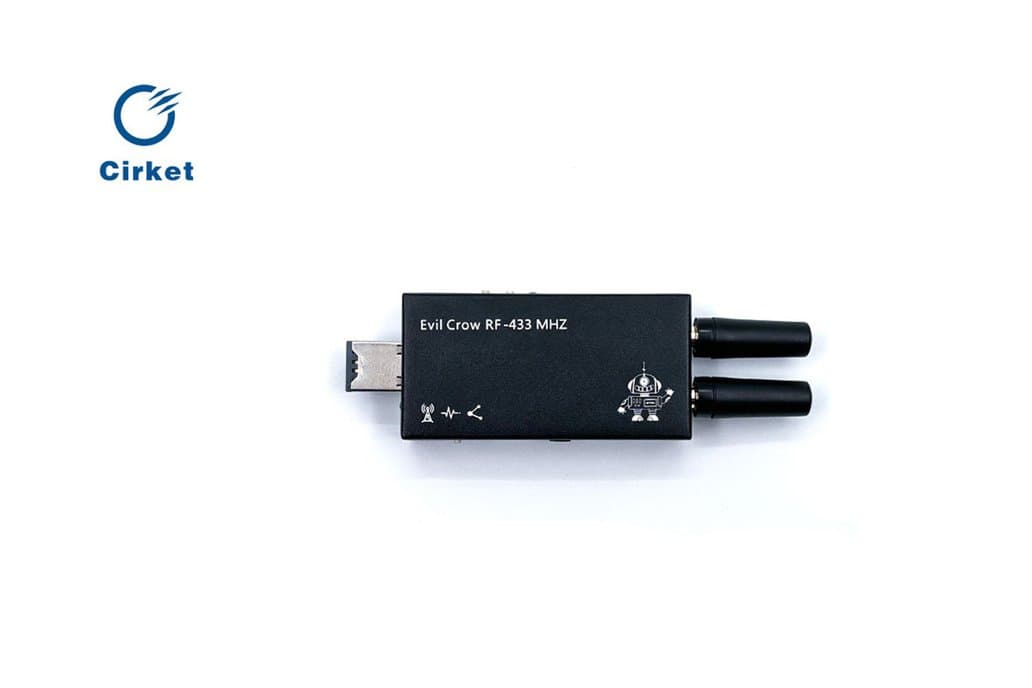
Evil Crow RF V2
Open-source RF security research tool with ESP32, dual CC1101 sub-GHz transceivers (300-928MHz), and NRF24L01 2.4GHz module for penetration testing, signal analysis, and replay attacks.
$41.39
Tap any value to browse matching devices
Specifications
Components
Espressif ESP32-D0WDQ6 Xtensa LX6 dual-core SoC running at 240MHz with 520KB SRAM, WiFi 802.11 b/g/n, Bluetooth 4.2/BLE, hardware crypto acceleration (AES/SHA/RSA), and ULP co-processor.
Texas Instruments CC1101 low-power sub-1GHz RF transceiver covering 300-348MHz, 387-464MHz, and 779-928MHz bands with configurable modulation (OOK, 2-FSK, 4-FSK, GFSK, MSK) and data rates up to 600kbps.
Second CC1101 module enabling simultaneous transmit and receive on different sub-GHz frequencies for real-time signal capture and replay.
Nordic Semiconductor nRF24L01 2.4GHz ISM-band transceiver enabling mousejacking attacks and 2.4GHz wireless communication at up to 2Mbps.
Silicon Labs CP2102N USB-to-UART bridge IC providing serial communication for firmware flashing and debug output via Micro-USB.
Diodes Incorporated AP2114H 1A low-dropout regulator converting 5V USB input to stable 3.3V for the ESP32 and RF modules.
Bus Interfaces
GPIO Map
Overview
The Evil Crow RF V2 is an open-source radiofrequency security research platform designed for penetration testers, red team operators, and cybersecurity enthusiasts. Built around the ESP32 microcontroller, it combines dual CC1101 sub-GHz transceivers with an NRF24L01 2.4GHz module to cover a wide range of RF attack and analysis scenarios.
The two CC1101 modules can be independently configured to transmit or receive on different frequencies simultaneously, enabling real-time signal capture and replay across the 300-348MHz, 387-464MHz, and 779-928MHz bands. The NRF24L01 module extends capabilities into the 2.4GHz range, supporting mousejacking and other wireless keyboard/mouse attacks. The device ships with a web-based control interface accessible over WiFi, allowing configuration of RX/TX parameters, signal logging, and jammer operation from any browser.
Evil Crow RF V2 stores captured signals on a microSD card and serves a responsive web panel at evilcrow-rf.local for real-time control. The firmware is fully open source and written in Arduino/C++, with an active community producing alternative ROMs that add features like BLE mobile app control, RF spectrum visualization, and Flipper Zero .sub file compatibility. The aluminum case variant provides durability and RF shielding for field use.
Use Cases
6RF Security Testing
Using RF transceivers to analyze, replay, and test the security of wireless radio frequency protocols and devices.
Penetration Testing
Security testing of embedded devices and IoT hardware to identify vulnerabilities through physical and electrical attacks.
Sub-GHz Research
Analyzing and interacting with sub-GHz wireless protocols and remote controls
Wireless Security Research
Tools and boards designed for wireless security auditing, RF analysis, and penetration testing across WiFi, Bluetooth, and Sub-GHz bands.
RF Signal Analysis
Analyzing and visualizing radio frequency signals across different bands using software-defined radio.
RF Experimentation
Experimenting with radio frequency circuits, antennas, and wireless protocols.
Explore more of the directory — popular use cases, firmware, and specs to browse next.