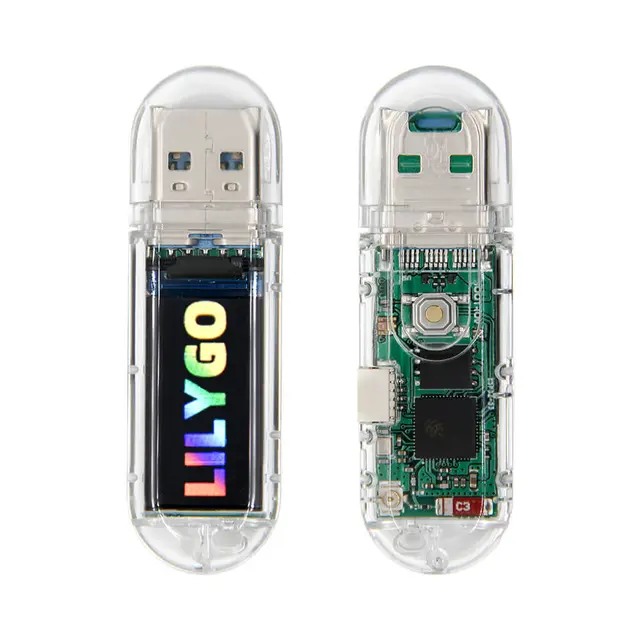
USB Army Knife — Portable Penetration Testing Dongle
Turns the LILYGO T-Dongle S3 into a Swiss Army knife for close-access penetration testing with BadUSB, WiFi attacks, BLE scanning, HID injection, and network implant capabilities.
Overview
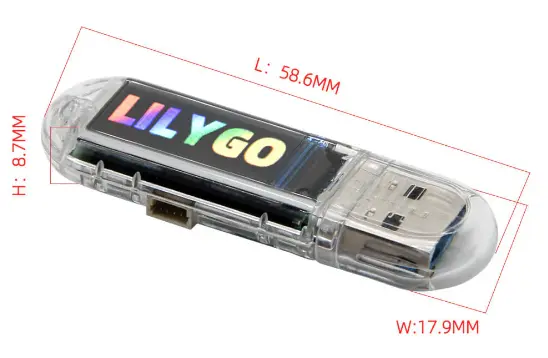
USB Army Knife is a highly popular open-source project (2,300+ GitHub stars) that transforms the LILYGO T-Dongle S3 into a multi-function close-access penetration testing tool. Plug it into any USB port and it can execute keystroke injection attacks, perform WiFi reconnaissance, scan Bluetooth devices, and act as a covert network implant — all from a tiny USB-A dongle with a color display.
Key Features
- BadUSB / Rubber Ducky: Execute pre-programmed keystroke injection payloads via USB HID emulation
- WiFi Attacks: Scan networks, create evil portals, beacon spam, and deauth detection
- BLE Scanner: Discover and fingerprint nearby Bluetooth Low Energy devices
- HID Injection: Automated keyboard/mouse input for payload delivery
- Network Implant: Act as a covert network device when plugged into a target
- Display Output: Real-time status on the T-Dongle S3's 0.96" color screen
Getting Started
Flash the firmware via PlatformIO or the web flasher. Load DuckyScript payloads onto the SD card. Plug the T-Dongle S3 into any target USB port to begin testing.
Why This Project
The T-Dongle S3's USB-A form factor makes it uniquely suited for close-access security testing — it looks like an ordinary USB stick. At under $10, it delivers capabilities that cost hundreds of dollars in commercial penetration testing hardware.