Infiltra RF Security Toolkit for T-Embed CC1101
An open-source multi-protocol security research firmware for the LILYGO T-Embed CC1101 with sub-GHz RF scanning, signal emulation, WiFi deauth, BLE spam, NFC cloning, and spectrum analysis — 159 stars on GitHub.
Overview
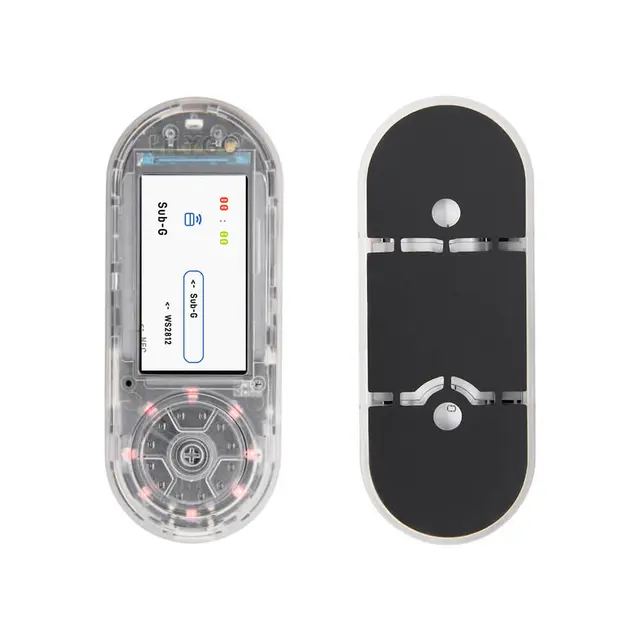
Infiltra Firmware is a community-built security testing toolkit specifically targeting the LILYGO T-Embed CC1101 alongside a range of other ESP32-based devices. It focuses on the sub-GHz capabilities of the onboard CC1101 transceiver for RF signal capture and replay, while also leveraging the ESP32-S3's WiFi and BLE radios for wireless network testing.
Features
The CC1101 module powers signal reading and emulation for capturing remote keyfobs, garage door openers, and similar devices in the 300–928 MHz range. A spectrum analyzer mode scans the frequency band and displays signal activity. WiFi tools include deauthentication attacks, beacon flooding, evil portal creation, and packet sniffing. BLE features cover device discovery and advertising spam. RFID/NFC reading and cloning is supported, as is IR remote capture and replay. A 2.4 GHz NRF24L01 mesh network tester is also included.
Build Details
Written in C++ (68%) and C (30.6%), licensed under GPL-2.0. The firmware has 159 GitHub stars and 11 forks with 154 commits from the development team. The T-Embed CC1101 is listed as a supported platform in the project documentation.