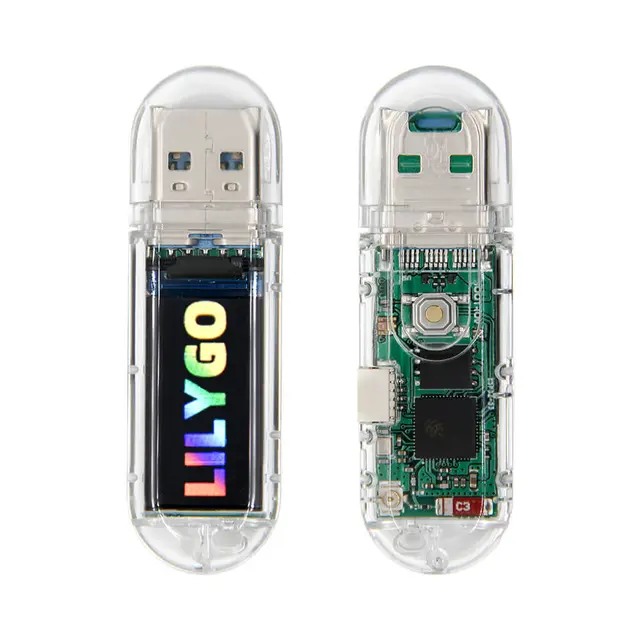
FRFD — First Responder Forensics Dongle on LILYGO T-Dongle S3
A portable CSIRT forensics tool on the LILYGO T-Dongle S3 that automates evidence collection from Windows, Linux, and macOS via USB HID keyboard emulation — with triage, containment, and collection modes shown on the 0.96" display.
Overview
FRFD (First Responder Forensics Dongle) turns the LILYGO T-Dongle S3 into a portable automated forensics toolkit for CSIRT incident responders. When plugged into a potentially compromised machine, the dongle appears as a USB keyboard and can automatically detect the operating system, open a terminal, execute a full forensic collection suite, and log all actions to SD card with SHA-256 integrity hashes following NIST SP 800-86 chain-of-custody guidelines.
Operating Modes
- Triage Mode — quick system assessment (~5 minutes)
- Collection Mode — full forensic artifact collection (~30 minutes): process dumps, registry autoruns, event logs, network state, DNS cache, ARP table, firewall rules
- Containment Mode — network isolation and security controls
- Analysis Mode — on-device IOC (indicator of compromise) matching
- HID Automation Mode — fully automated collection; no manual script execution required
HUD Display
The T-Dongle S3's 0.96" screen shows a compact status panel with current mode, detected OS, risk level, progress bar, elapsed time, and network status.
Technical Details
Built with PlatformIO targeting the T-Dongle S3's ESP32-S3 with USB OTG for HID keyboard emulation. Evidence is collected to SD card. The project is in alpha stage (v0.4.0) and actively developed. Requires a FAT32 SD card. Build and flash using pio run --target upload.