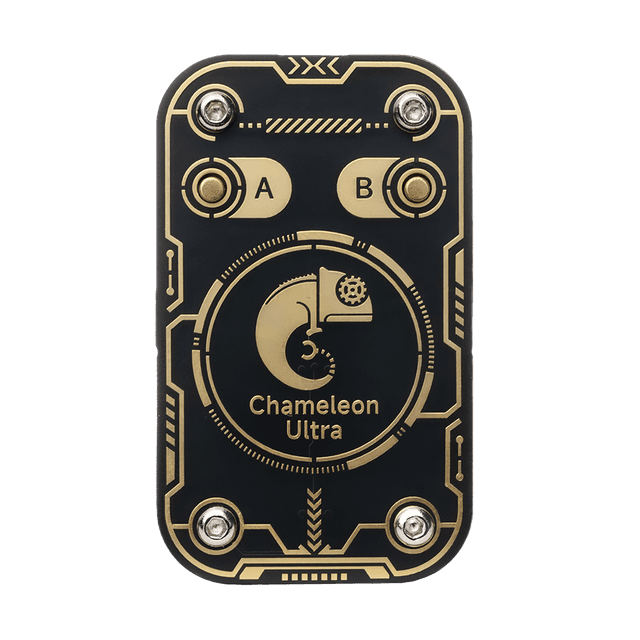
ChameleonUltra for Red Team Operations — Field Guide
Practical field guide by Brian Harris (Covert Access Team) covering the ChameleonUltra for physical penetration testing and red team engagements. Evaluates real-world badge cloning, discreet carry, and operational use alongside Proxmark3.
ChameleonUltra for Red Team Operations
A field-focused guide by Brian Harris of the Covert Access Team evaluating the ChameleonUltra's practical applications for physical security assessments, red team operations, and penetration tests involving badge systems.
Key Insights
Operational Advantages
- Ultra-compact form factor — fits in pockets or badge lanyards, far more discreet than Flipper Zero or Proxmark3
- 8 dual card slots — pre-load multiple cloned credentials for different access points
- Programmable buttons — execute operations independently of the app for quick field use
- 6-month battery life — reliable for extended engagements without charging
Core Strength
The article emphasizes that the ChameleonUltra "succeeds by doing one thing very well: high-frequency RFID cloning and emulation." Unlike multi-purpose tools, it focuses entirely on being the best portable RFID emulator.
Recommended Usage
Harris positions the ChameleonUltra as either:
- A primary tool for lightweight badge cloning operations
- A backup companion to Proxmark3 for comprehensive physical security assessments
Comparison with Alternatives
- More discreet than Flipper Zero or iCopy-XS
- Half the price of Proxmark3 with superior emulation
- Cracking capabilities equal to Proxmark3 for MIFARE Classic
Author
Brian Harris writes for the Covert Access Team Substack, covering tools and techniques for physical security professionals.